Zero Trust · Identity · AI security
Securing the agentic era in the Microsoft cloud.
Hands-on research on how attackers abuse identities, tokens and AI agents, and how to stop them with Entra, Purview, Defender and Sentinel. Every post is tested in a real lab.
// detect: new secret on a privileged app
AuditLogs
| where OperationName has "Update application"
| where TargetResources has "KeyCredentials"
| join kind=inner (PrivilegedApps) on AppId
| project TimeGenerated, InitiatedBy, AppId
The series
Zero Trust for AI
From prerequisites to detection: verify explicitly, use least privilege and assume breach, applied to AI agents with Agent 365, Entra Agent ID, Conditional Access, ID Governance and Purview.
Part 01
Coming soon
Why AI needs Zero Trust
The three principles, applied to agents
About
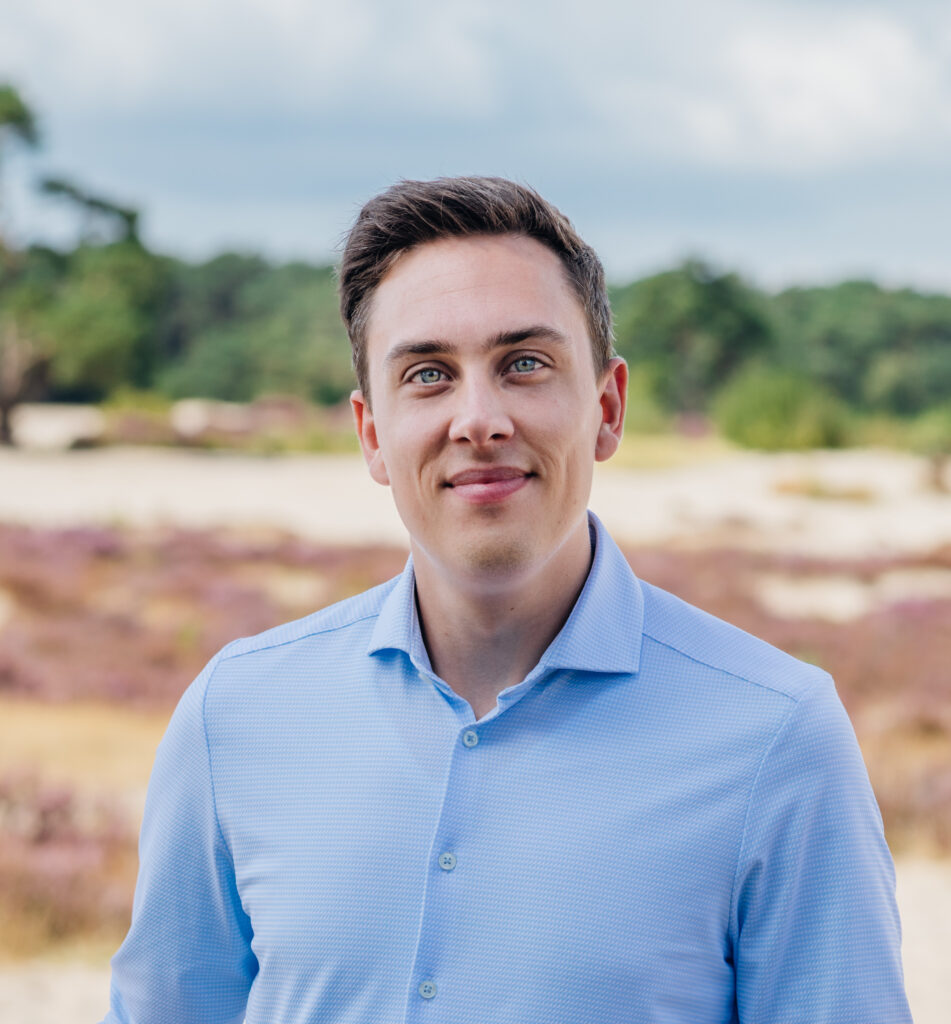
Hi, I’m Stien.
I’m a security consultant with over 10 years of experience, working only with Microsoft technology. I help organisations harden their cloud with Entra ID, Defender, Sentinel and Purview. I grew up on in Zeeland Netherlands, where we’ve been building defences against the tide for centuries. Today I build them against attackers.
LinkedIn ·